Agent identity and governance for enterprise AI
Autonomy without overreach.
HyperShell puts a governed Envelope around every agent task, in your own infrastructure with OpenShell or your AWS account.
- read test-logsALLOWED
- write prod-configBLOCKED
- request billing-apiAPPROVAL SENT
- call claude-sonnetALLOWED
Sample data.
The problem
Personal AI assistants took off. Autonomous agents stall on access control.
People supervise assistants. Autonomous agents choose their own steps. Enterprises need to grant access without approving every action.
- Authority
- Who granted permission, and for which task?
- Every new workflow waits on a manual access review.
- Limits
- What can the agent read, change or delegate?
- Broad credentials put critical data at risk, and model calls and retries run up spend.
- Evidence
- Did the agent stay within those limits?
- Logs show what was called, not whether the agent stayed in scope.
The product
An Envelope defines what an agent can do.
One Envelope per task, tied to the person or organization that granted it, and enforced the same way on any supported runtime.
Person or organization
via your enterprise IdP
Agent Envelope
Tools and data
Approved systems and resources.
Actions
What the agent may read or change.
Delegation
Helpers get the same or narrower limits. More needs new approval.
Models and spend
Approved models and a spending limit.
Enforced at
Agent sandbox
MCP gateway
LLM gateway
Run evidence
linked back to the grant
01
Define the authority
Identify the agent and the person or organization granting authority. Define its task, permitted actions, resources and limits.
02
Enforce the limits
Block actions outside the Envelope. Sub-agents inherit its limits. More authority needs new approval.
03
Show what happened
Link actions and outcomes to the original grant, so you can review whether the agent stayed in scope.
The platform
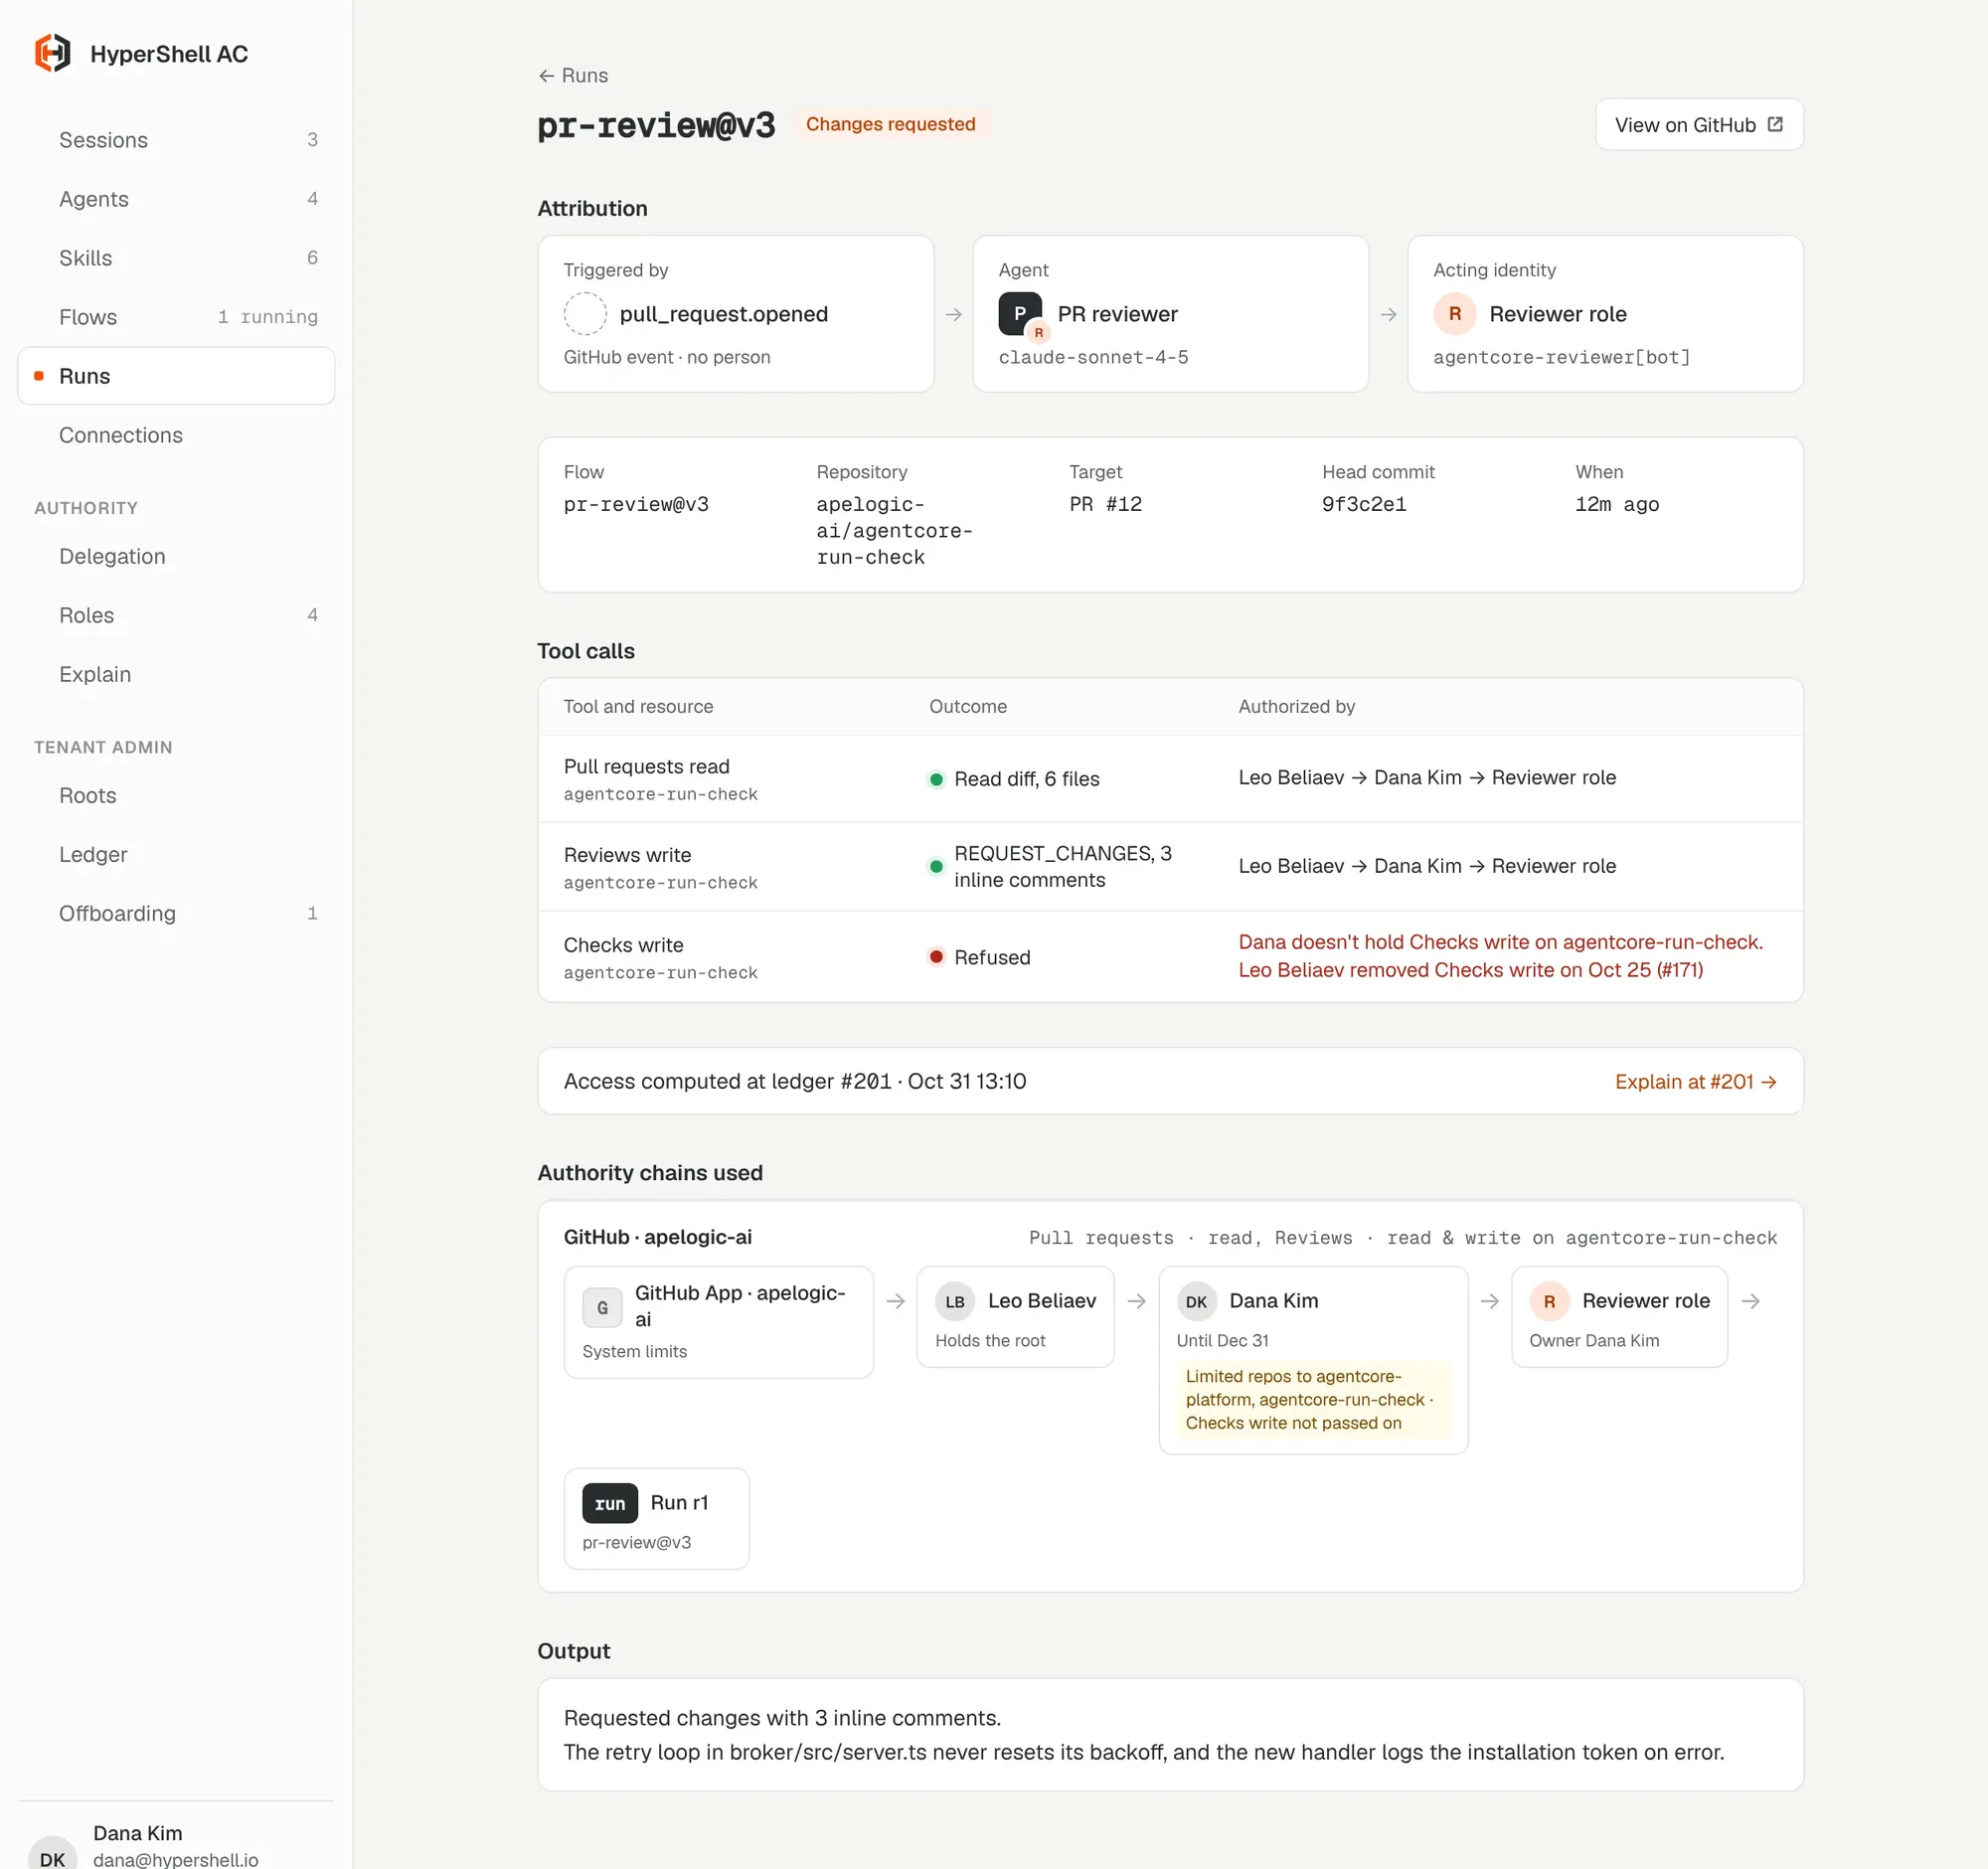
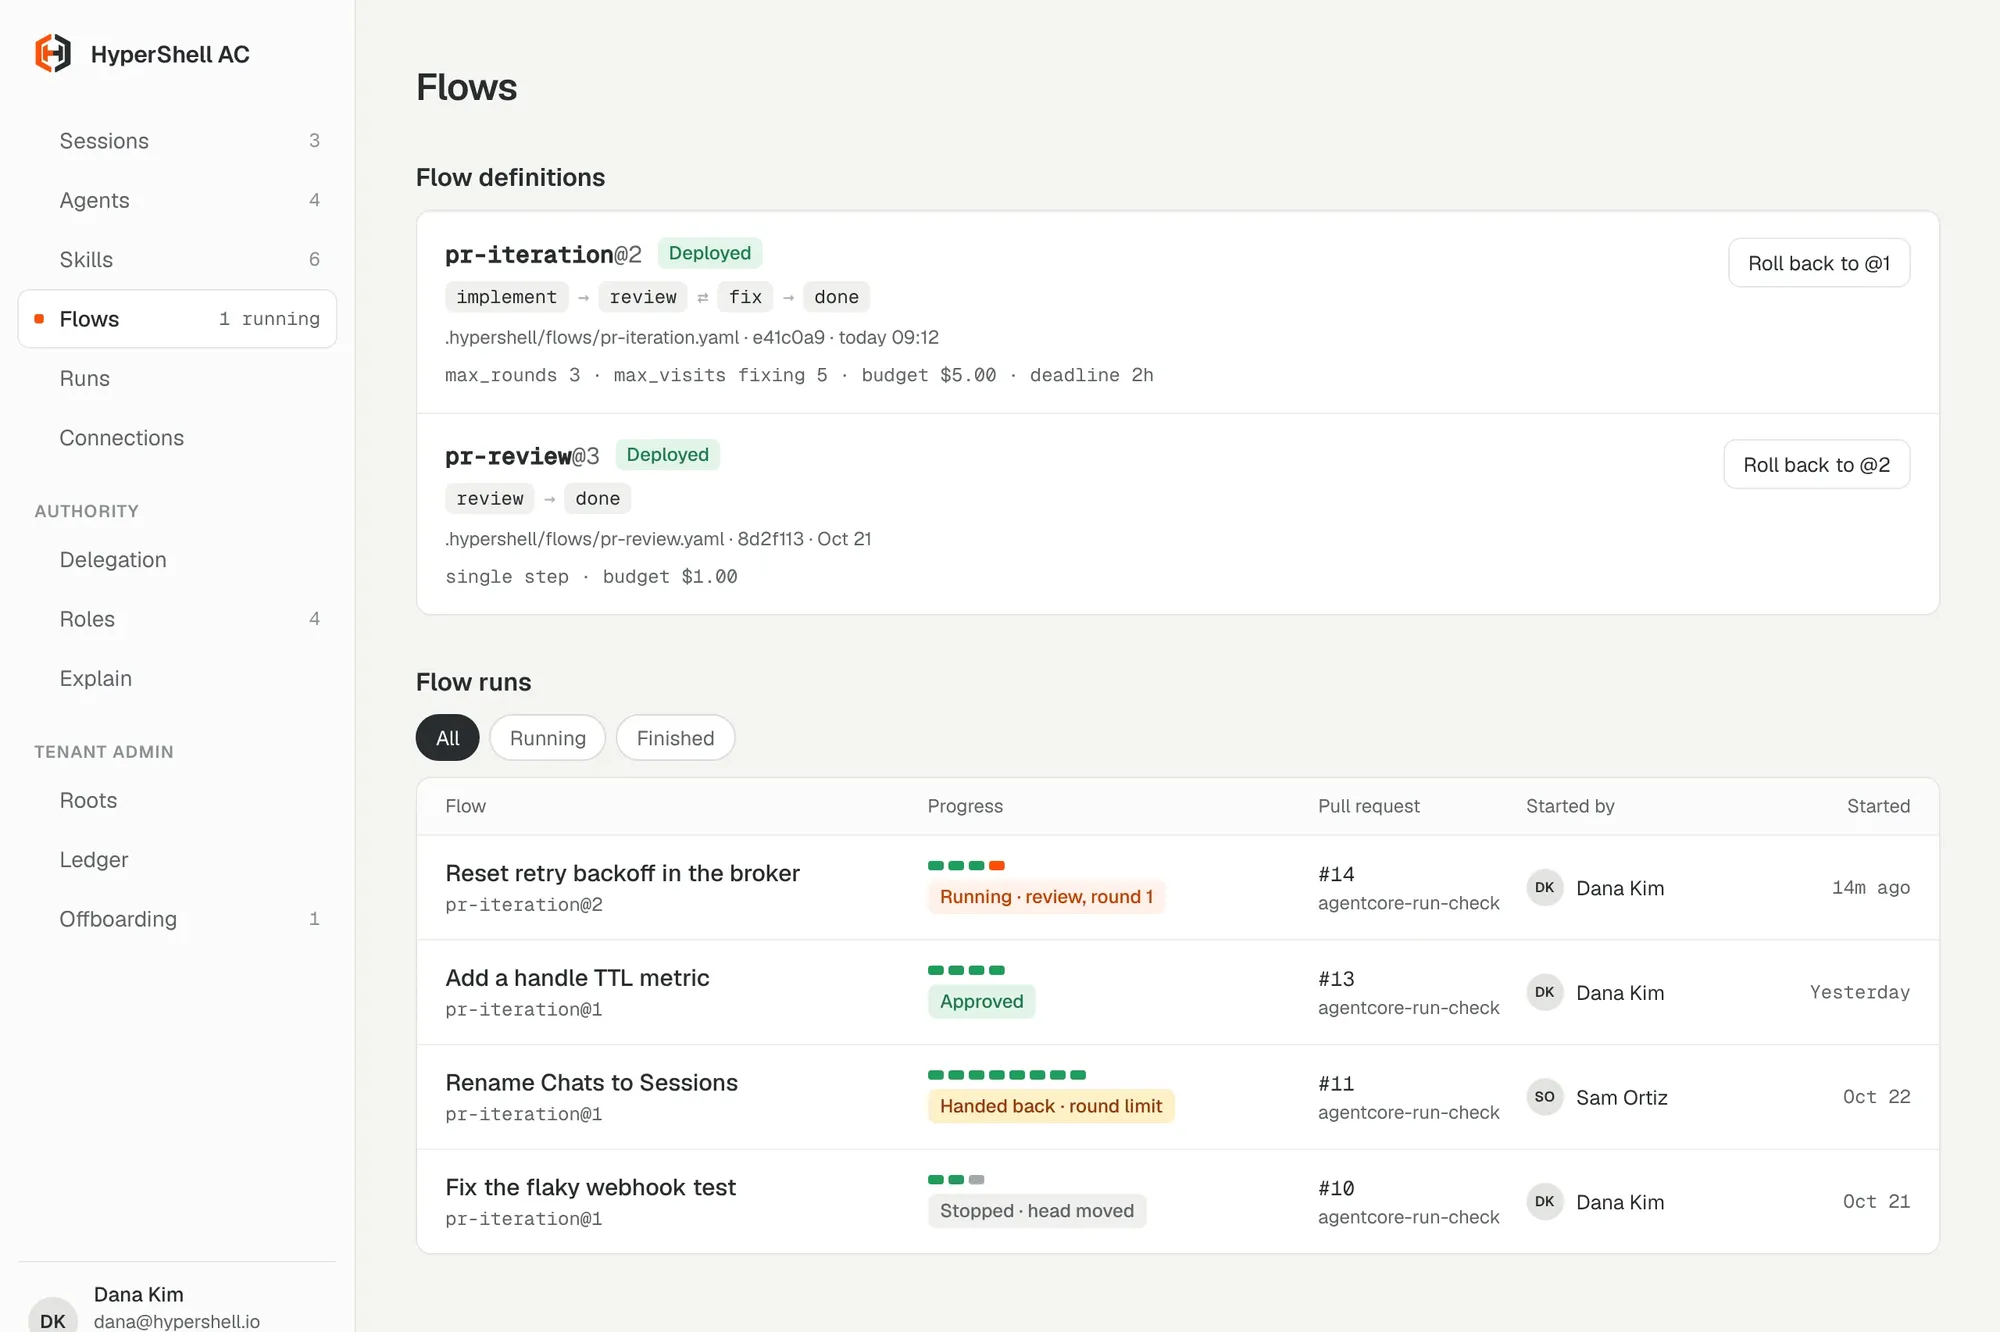
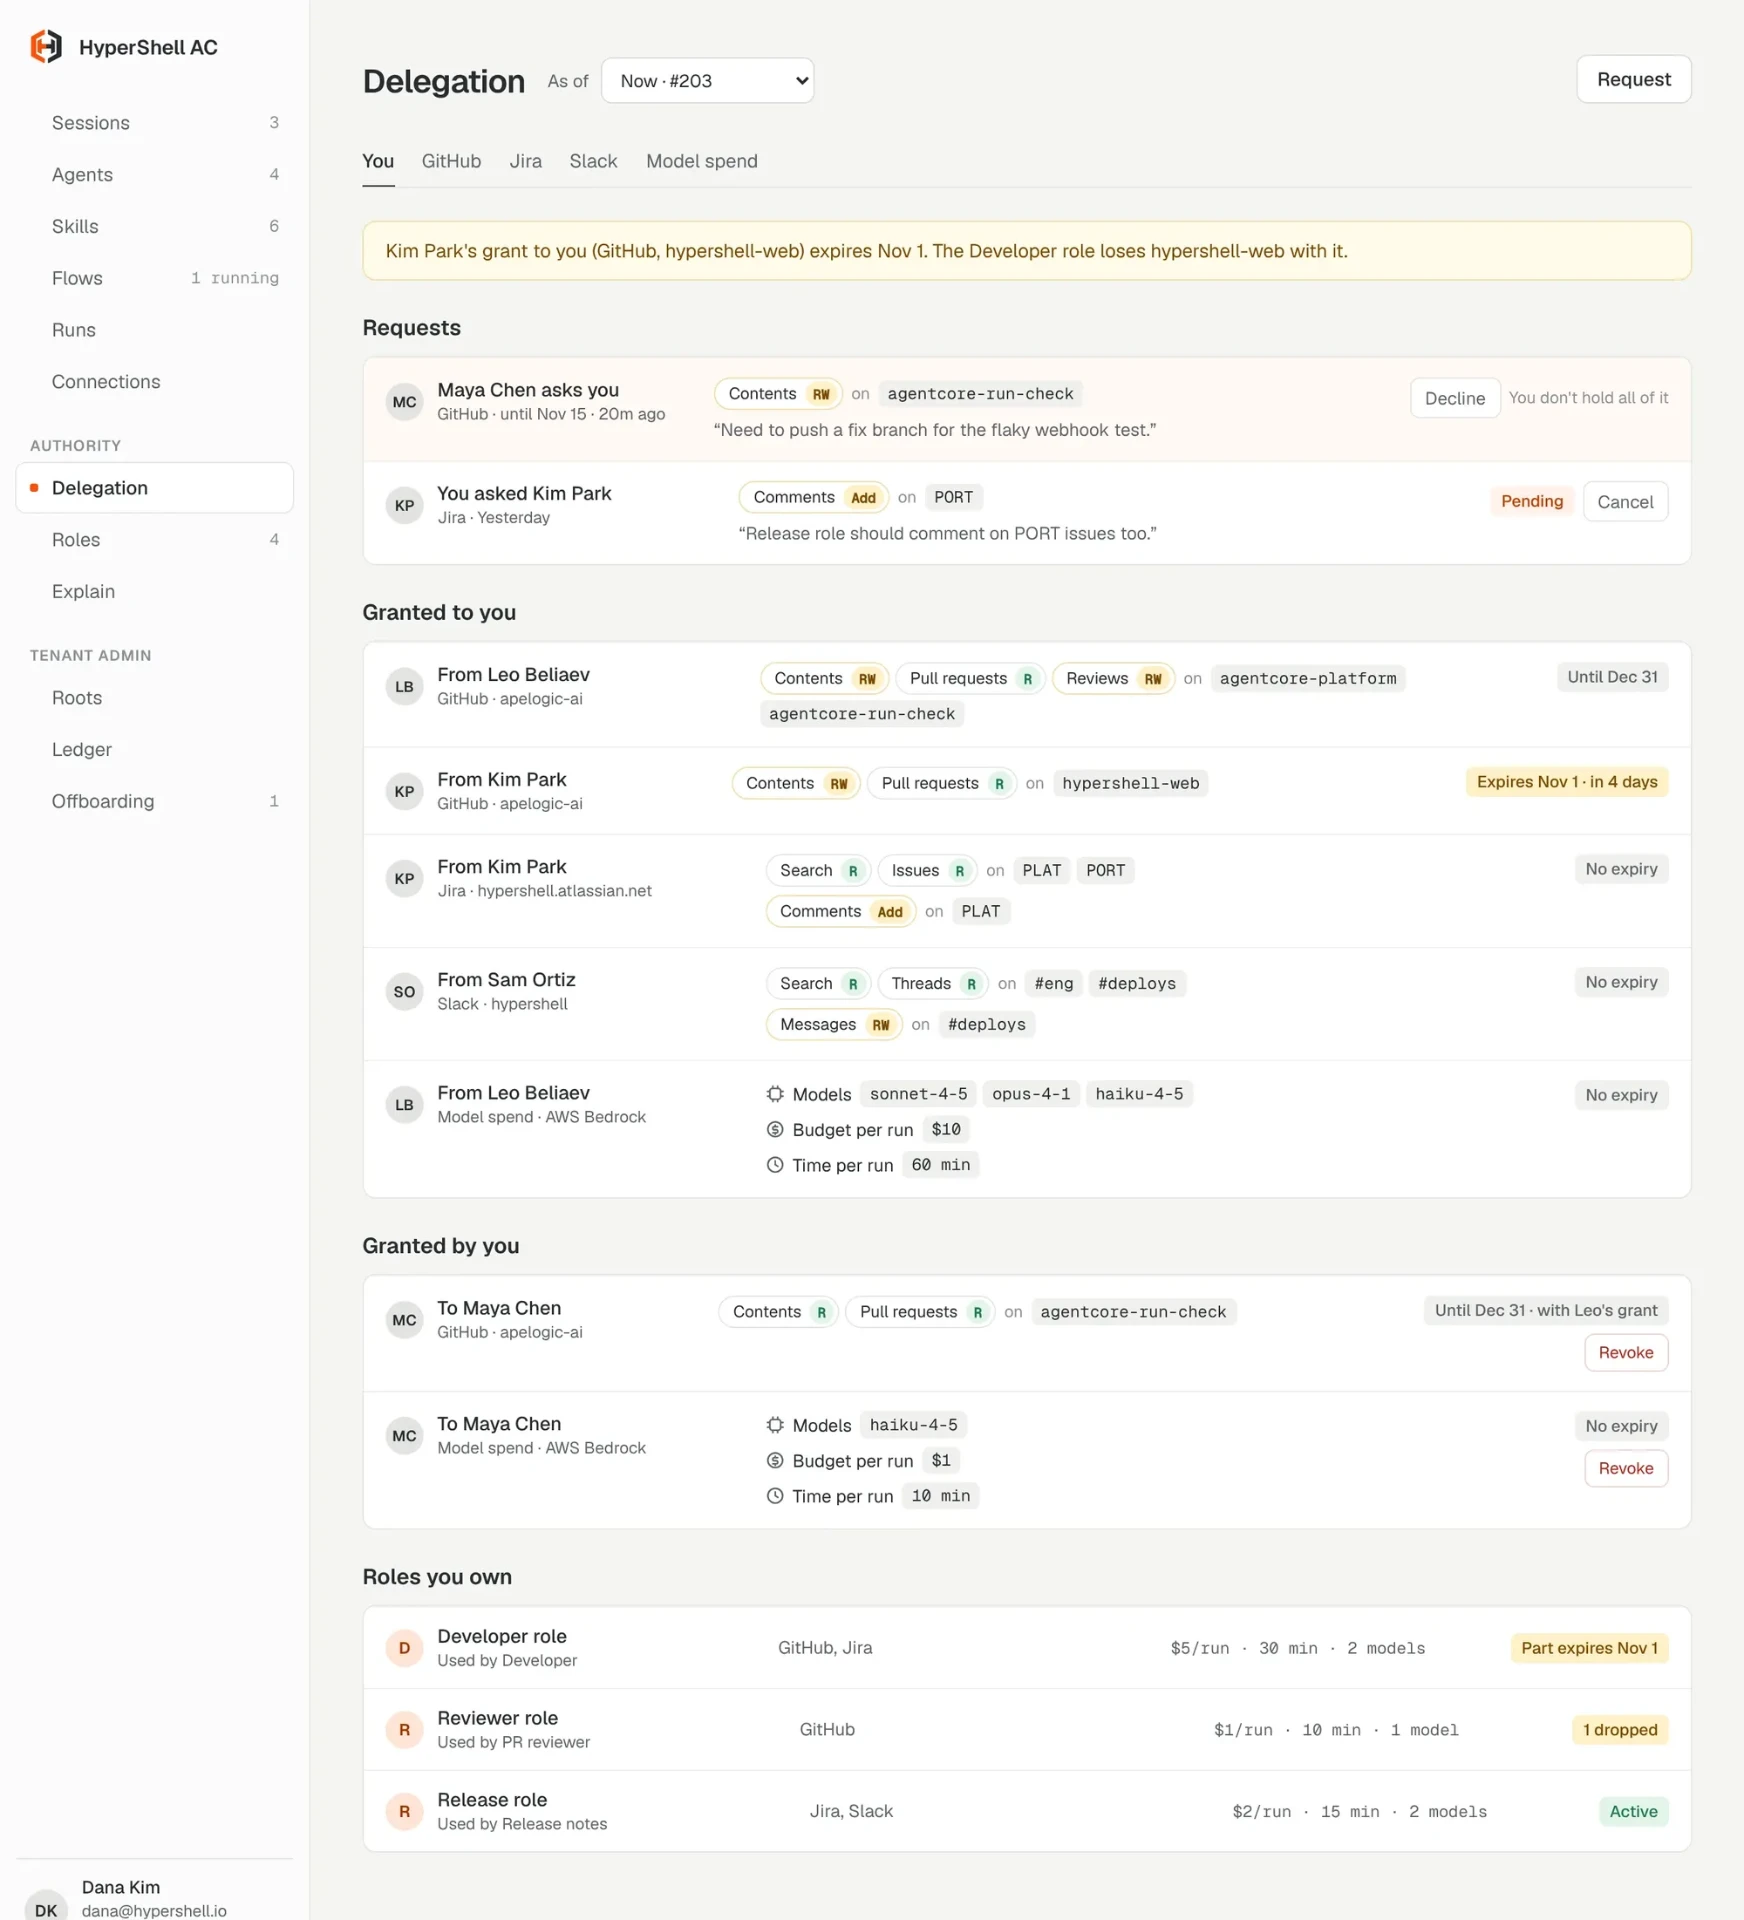
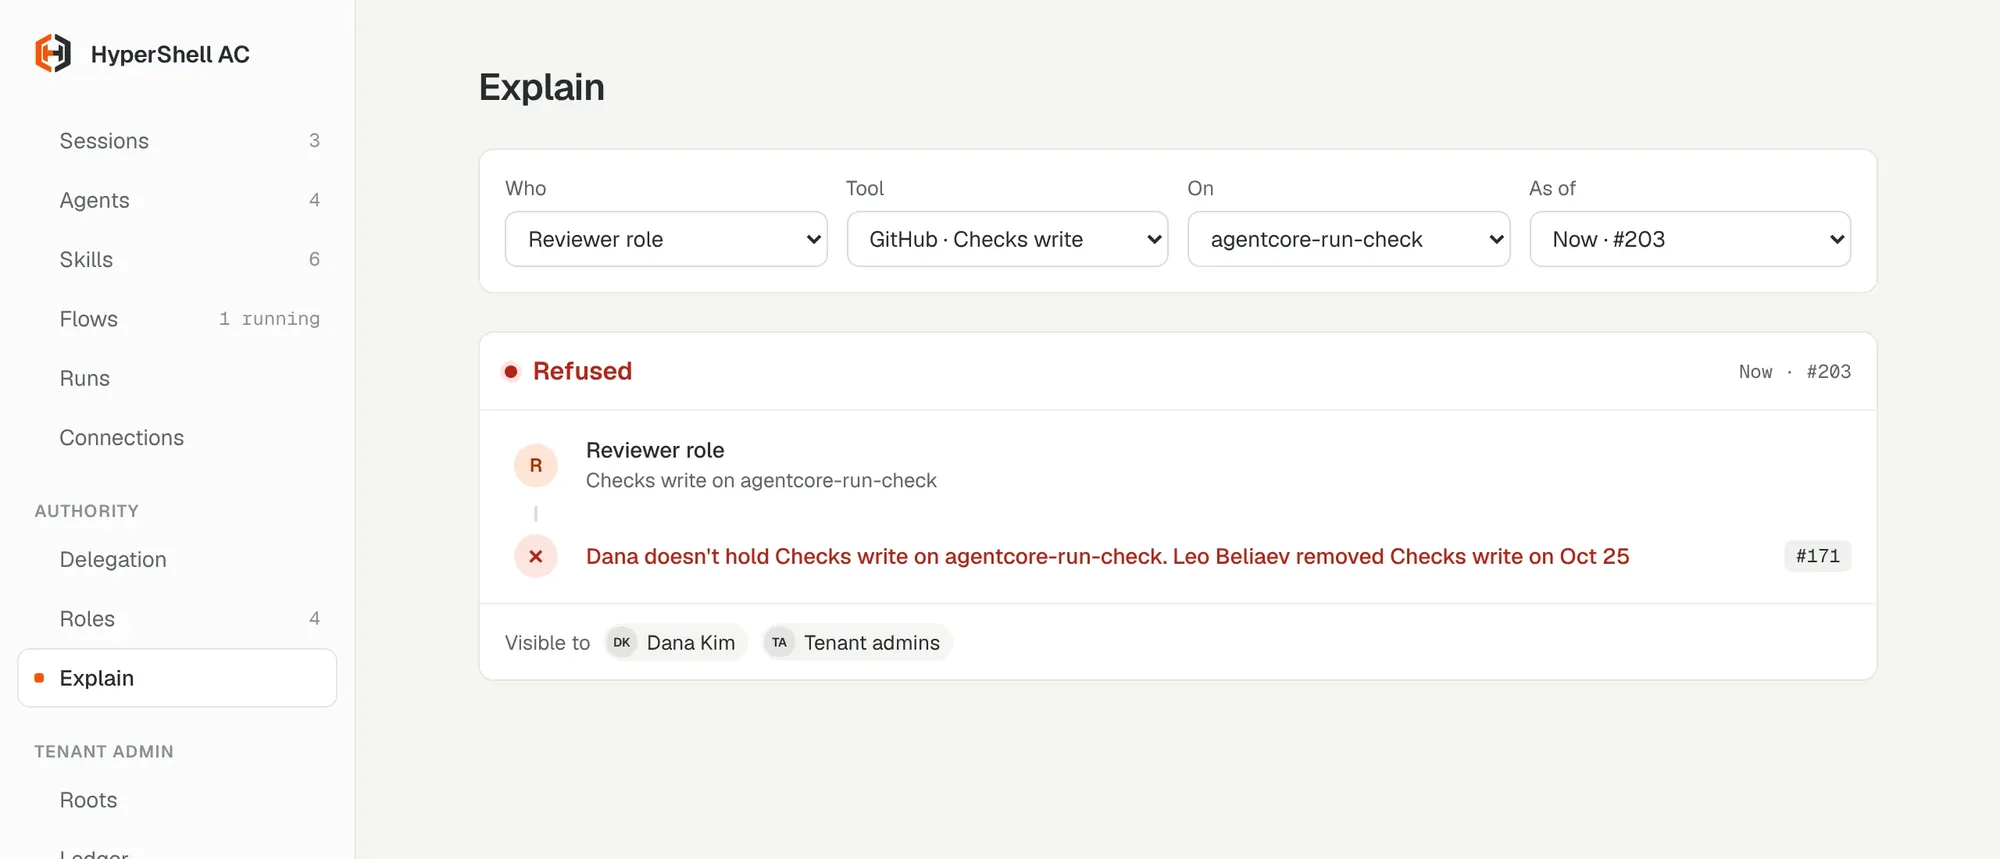
Every grant, request and exception in one place.
Engineers request access within a template ceiling and inspect every run. Administrators set the ceilings and review only the exceptions.
See the platform walkthroughWhy HyperShell
Gateways see tool calls. HyperShell governs the whole task.
Agent controls overlap. The difference is what authority is scoped to and where it is enforced.
Identity provider tokens
Agent gateways
HyperShell
One Envelope, end to end
HyperShell works with your existing identity provider and runtimes rather than replacing them. Category comparison based on vendor documentation.
Deployment
- NVIDIA OpenShell · your data center
- Amazon Bedrock AgentCore · your AWS account
Works with your existing identity provider.
Use cases
Governed workflows across the enterprise.
Illustrative first workflows to scope with your team.
Customer example
Governed analytics at Helium Mobile
Less dashboard data-ops work
~60%
From kickoff to handoff
Under 2 months

"HyperShell gave our agents safe, governed access to the data warehouse. Employees stopped waiting days for answers."
How we start
A supported path to your first governed workflow.
01
No costScope
Workflow scoping session
Pick one workflow. Agree on its access and spending limits and a measurable success criterion.
02
Scoped separatelyDeploy and build
Implementation engagement
HyperShell engineers deploy the platform in your environment, connect approved systems and build the first workflow with your team.
Run and expand
Annual subscription
Governance platform, supported runtime management and ongoing support. Add workflows, users and agents as you grow.
Run in your environment. Build on a foundation your team can extend.
Team
A team that has built and sold open source infrastructure companies, and operated inside large enterprises.
Boris Renski
CEO
Serial open source infrastructure founder. Co-founded Mirantis (acquired by IREN) and FreedomFi (acquired by Nova Labs).
Leo Beliaev
CTO
Engineering leader from Cisco and Dell, and former CEO of Okko, a leading European video streaming platform.
Chris Clason
CRO
AI and infrastructure executive with 22+ years, including leadership roles at Mirantis, Digital Asset and AMD.
Alex Gelf
VP, Customer Engineering
Delivery leader across Silicon Valley and Europe, most recently General Manager at Inventra, a European HR-tech company.
Schedule a workflow scoping session.
Bring a workflow owner and a security or platform lead. Leave with a proposed workflow scope, access and spending limits, and a measurable success criterion.